

The EU is telling cryptocurrency {hardware} and software program pockets suppliers that they’ve 24 hours from consciousness to report actively exploited bugs or extreme safety vulnerabilities affecting their merchandise.
The measure is a part of the EU’s Cyber Resilience Act (CRA), which took impact on Friday, in accordance with an announcement from the European Fee.
Producers should submit an early warning for extreme vulnerabilities inside 24 hours, adopted by a full notification inside 72 hours. A ultimate report will likely be required 14 days after corrective or mitigating measures can be found and inside one month for extreme incidents.
The EC mentioned the brand new reporting necessities purpose to raised defend shoppers and companies from cyber threats. The measure extends to all merchandise “with digital parts made accessible within the EU” and builds on the EU’s broader cybersecurity technique.
Cointelegraph has approached the European Fee for extra particulars surrounding the cybersecurity measures.
Associated: German finance ministry proposes 25% crypto tax beginning 2028: Report
Fines might attain $17 million
Firms that fail to stick to the cybersecurity measures beneath Articles 13 and 14 could face an administrative high quality of as much as 15 million euros ($17.3 million) or 2.5% of worldwide annual turnover, relying on which determine is larger, in accordance with the penalties part of the ultimate draft.
Supplying incorrect, incomplete or deceptive data may even topic corporations to an administrative high quality of as much as 5 million euros.
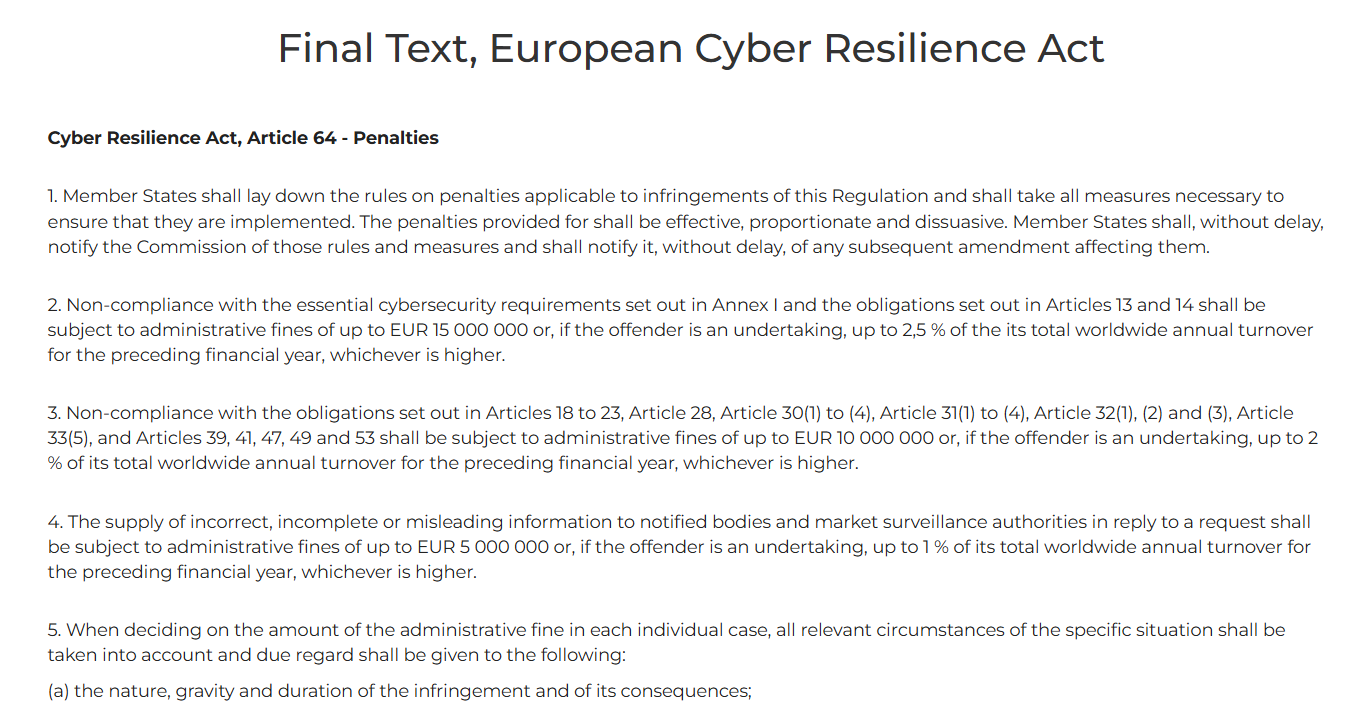
Excerpt from Last Textual content, European Cyber Resilience Act. Supply: European-Cyber-Resilience-Act.com
The measure was revealed weeks after two standard {hardware} pockets suppliers disclosed person information breaches that would result in phishing or social engineering makes an attempt.
On Sept. 4, {hardware} pockets supplier Trezor revealed that an extra 67,000 US prospects have been in danger from the information breach suffered by its transport supplier, ShipMonk, exceeding the initially estimated 14,000 customers.
On Wednesday, Trezor and BitBox warned customers about phishing emails disguised as pressing safety notices after suspected compromises involving third-party e-mail providers.
In June, Layer-1 blockchain community Zilliqa warned {that a} vulnerability within the Zilliqa Ledger app might enable attackers to get well customers’ non-public keys utilizing publicly accessible onchain information.
Cointelegraph has approached pockets makers Trezor and Ledger for touch upon how pockets suppliers would adjust to the brand new reporting necessities.
Journal: How Hong Kong is popping tokenized bonds into actual market infrastructure